MANAGED DATA DETECTION AND RESPONSE

24x7 experts who stop data breaches for you

Varonis MDDR pairs AI-powered detection with elite incident responders. We investigate every alert, hunt every threat, and stay until the breach is contained.

30-MIN SLA
EXPERT TEAM
DFIR INCLUDED
Book a demo
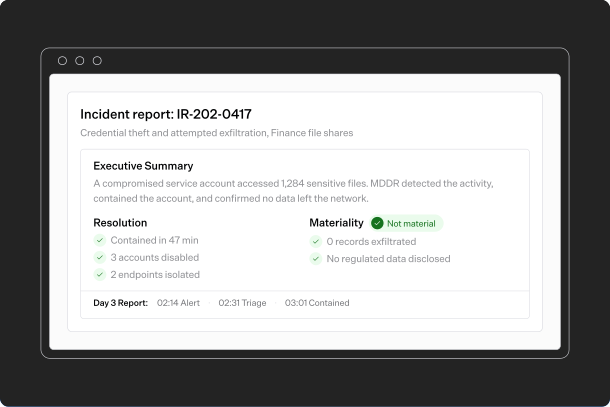
Sample Incident Report

Trusted by 8,000+ customers

WHY MDDR

Any MDR service can spot a threat. We stop them from getting to your data.

Varonis MDDR monitors your critical data and AI agents. When something happens, you can answer the question that matters: was this a material breach?

Detect what others miss

We see who touched sensitive data and how, across identity, cloud, endpoint, and network. Catch insiders and attackers that slip past EDR.

We see who touched sensitive data and how, across identity, cloud, endpoint, and network. Catch insiders and attackers that slip past EDR.

Respond in minutes

Our experts investigate ransomware in under 30 minutes and every other alert in under two hours. It's in the contract.

Our experts investigate ransomware in under 30 minutes and every other alert in under two hours. It's in the contract.

Recover with no surprise bills

Full breach response, forensics, and reporting come with MDDR. No retainers. No hour banks. No extra fee for the report.

Full breach response, forensics, and reporting come with MDDR. No retainers. No hour banks. No extra fee for the report.

Reduce your blast radius

Focus on the permissions and exposed data that could increase the impact of a breach.

Accelerate compliance

Bring data discovery, access visibility, and activity monitoring together to support your compliance program.

AI SPEED, HUMAN JUDGMENT

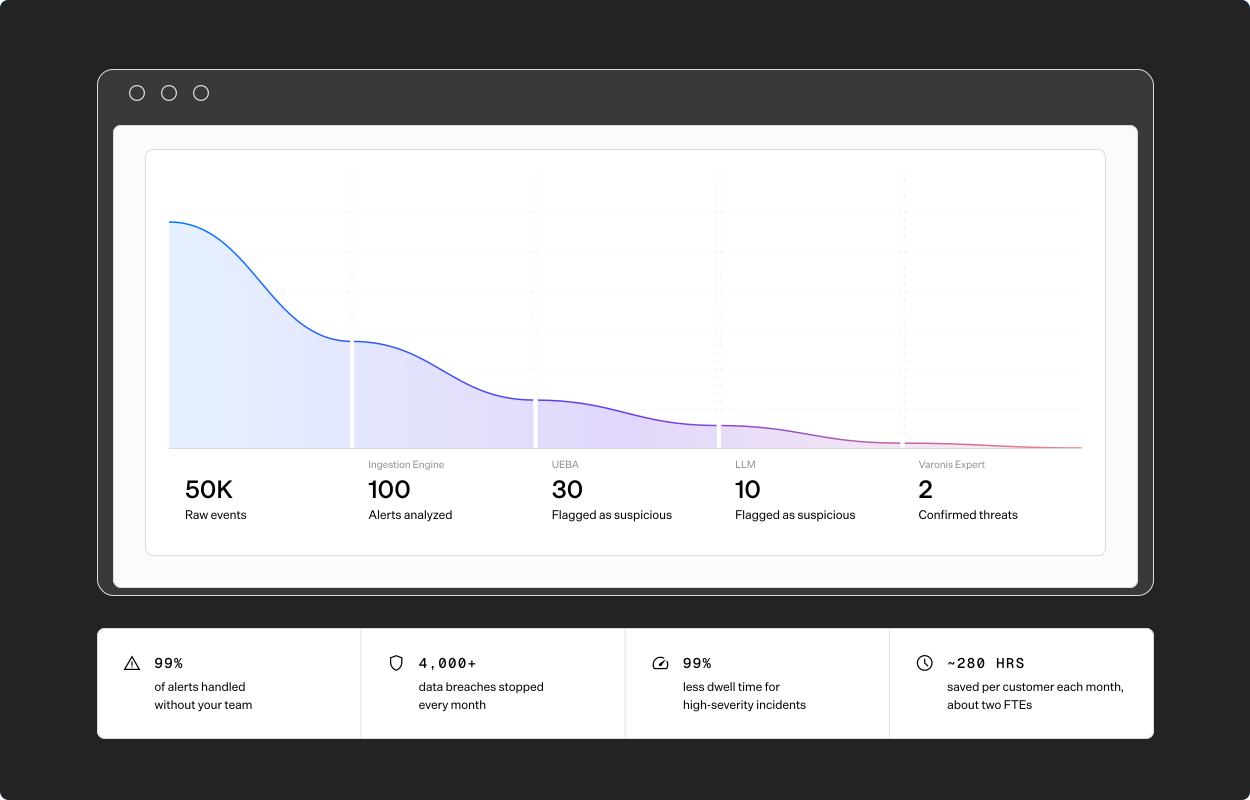
From 5,000,000 eventsto the 2 alerts that matter.

Varonis AI cuts through the noise. Our triage agent identifies true positives. Then a Varonis expert confirms every threat before it reaches you. Your team only hears about real escalations.

Get a demo
Sample Incident Report
Varonis dataflows dashboard
Varonis product overview
auto
image

WORLD-CLASS BREACH RESPONSE

On your worst day,we stay until it's over.

Our forensics team came from the world's top IR firms and cyber warfare units. They do the work of a high-cost IR retainer, and it's already part of your MDDR license.

Digital forensics and incident response

We hunt across every source you have: EDR, SIEM, email, network, firewalls, and DNS. Our own tools capture disk images, memory, and logs. No data source is out of scope.

Incident response security platform integrations

Executive and legal reporting

During an active incident, you get real-time briefings. Leadership gets an executive summary. Legal and regulators get a full post-mortem readout.

Executive incident report and resolution summary

"It’s not just a tool, it’s a relationship. We always feel Varonis is there for us, and they’ve never wavered. That’s why I love Varonis."

Brian Valiquette

Director of Information Security Risk & Compliance

​
See full case study

"Leveraging Varonis to properly permission our files gives me the confidence to move forward with AI adoption."

‍

Jacob Lorz

VP Information Technology & CISO

​
See full case study

“The only reason I'm prepared and feel safe in recommending our AI products through AI Governance Committee is because we have Varonis.”

‍

Jim Bowie

CISO

​
See full case study

Varonis Threat Labs

Varonis Threat Labs finds new attack techniques in the cloud and AI apps you use every day. What they find becomes new detections in MDDR.

Research by Varonis Threat Labs

Proactive threat hunting

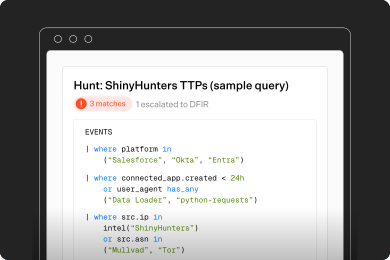
We don't wait for an alert. Our team hunts for hidden attackers and persistent threats across your environment.

Proactive threat hunting query and findings

Security posture assessments

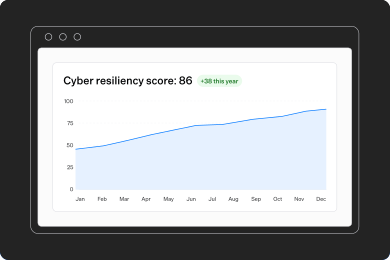
Monthly assessments show where your data is exposed and what to fix first. Your risk goes down over time, not just your alert count.

Cyber resiliency score and security posture improvement

TRUSTED

Trusted by thousands of enterprise customers.

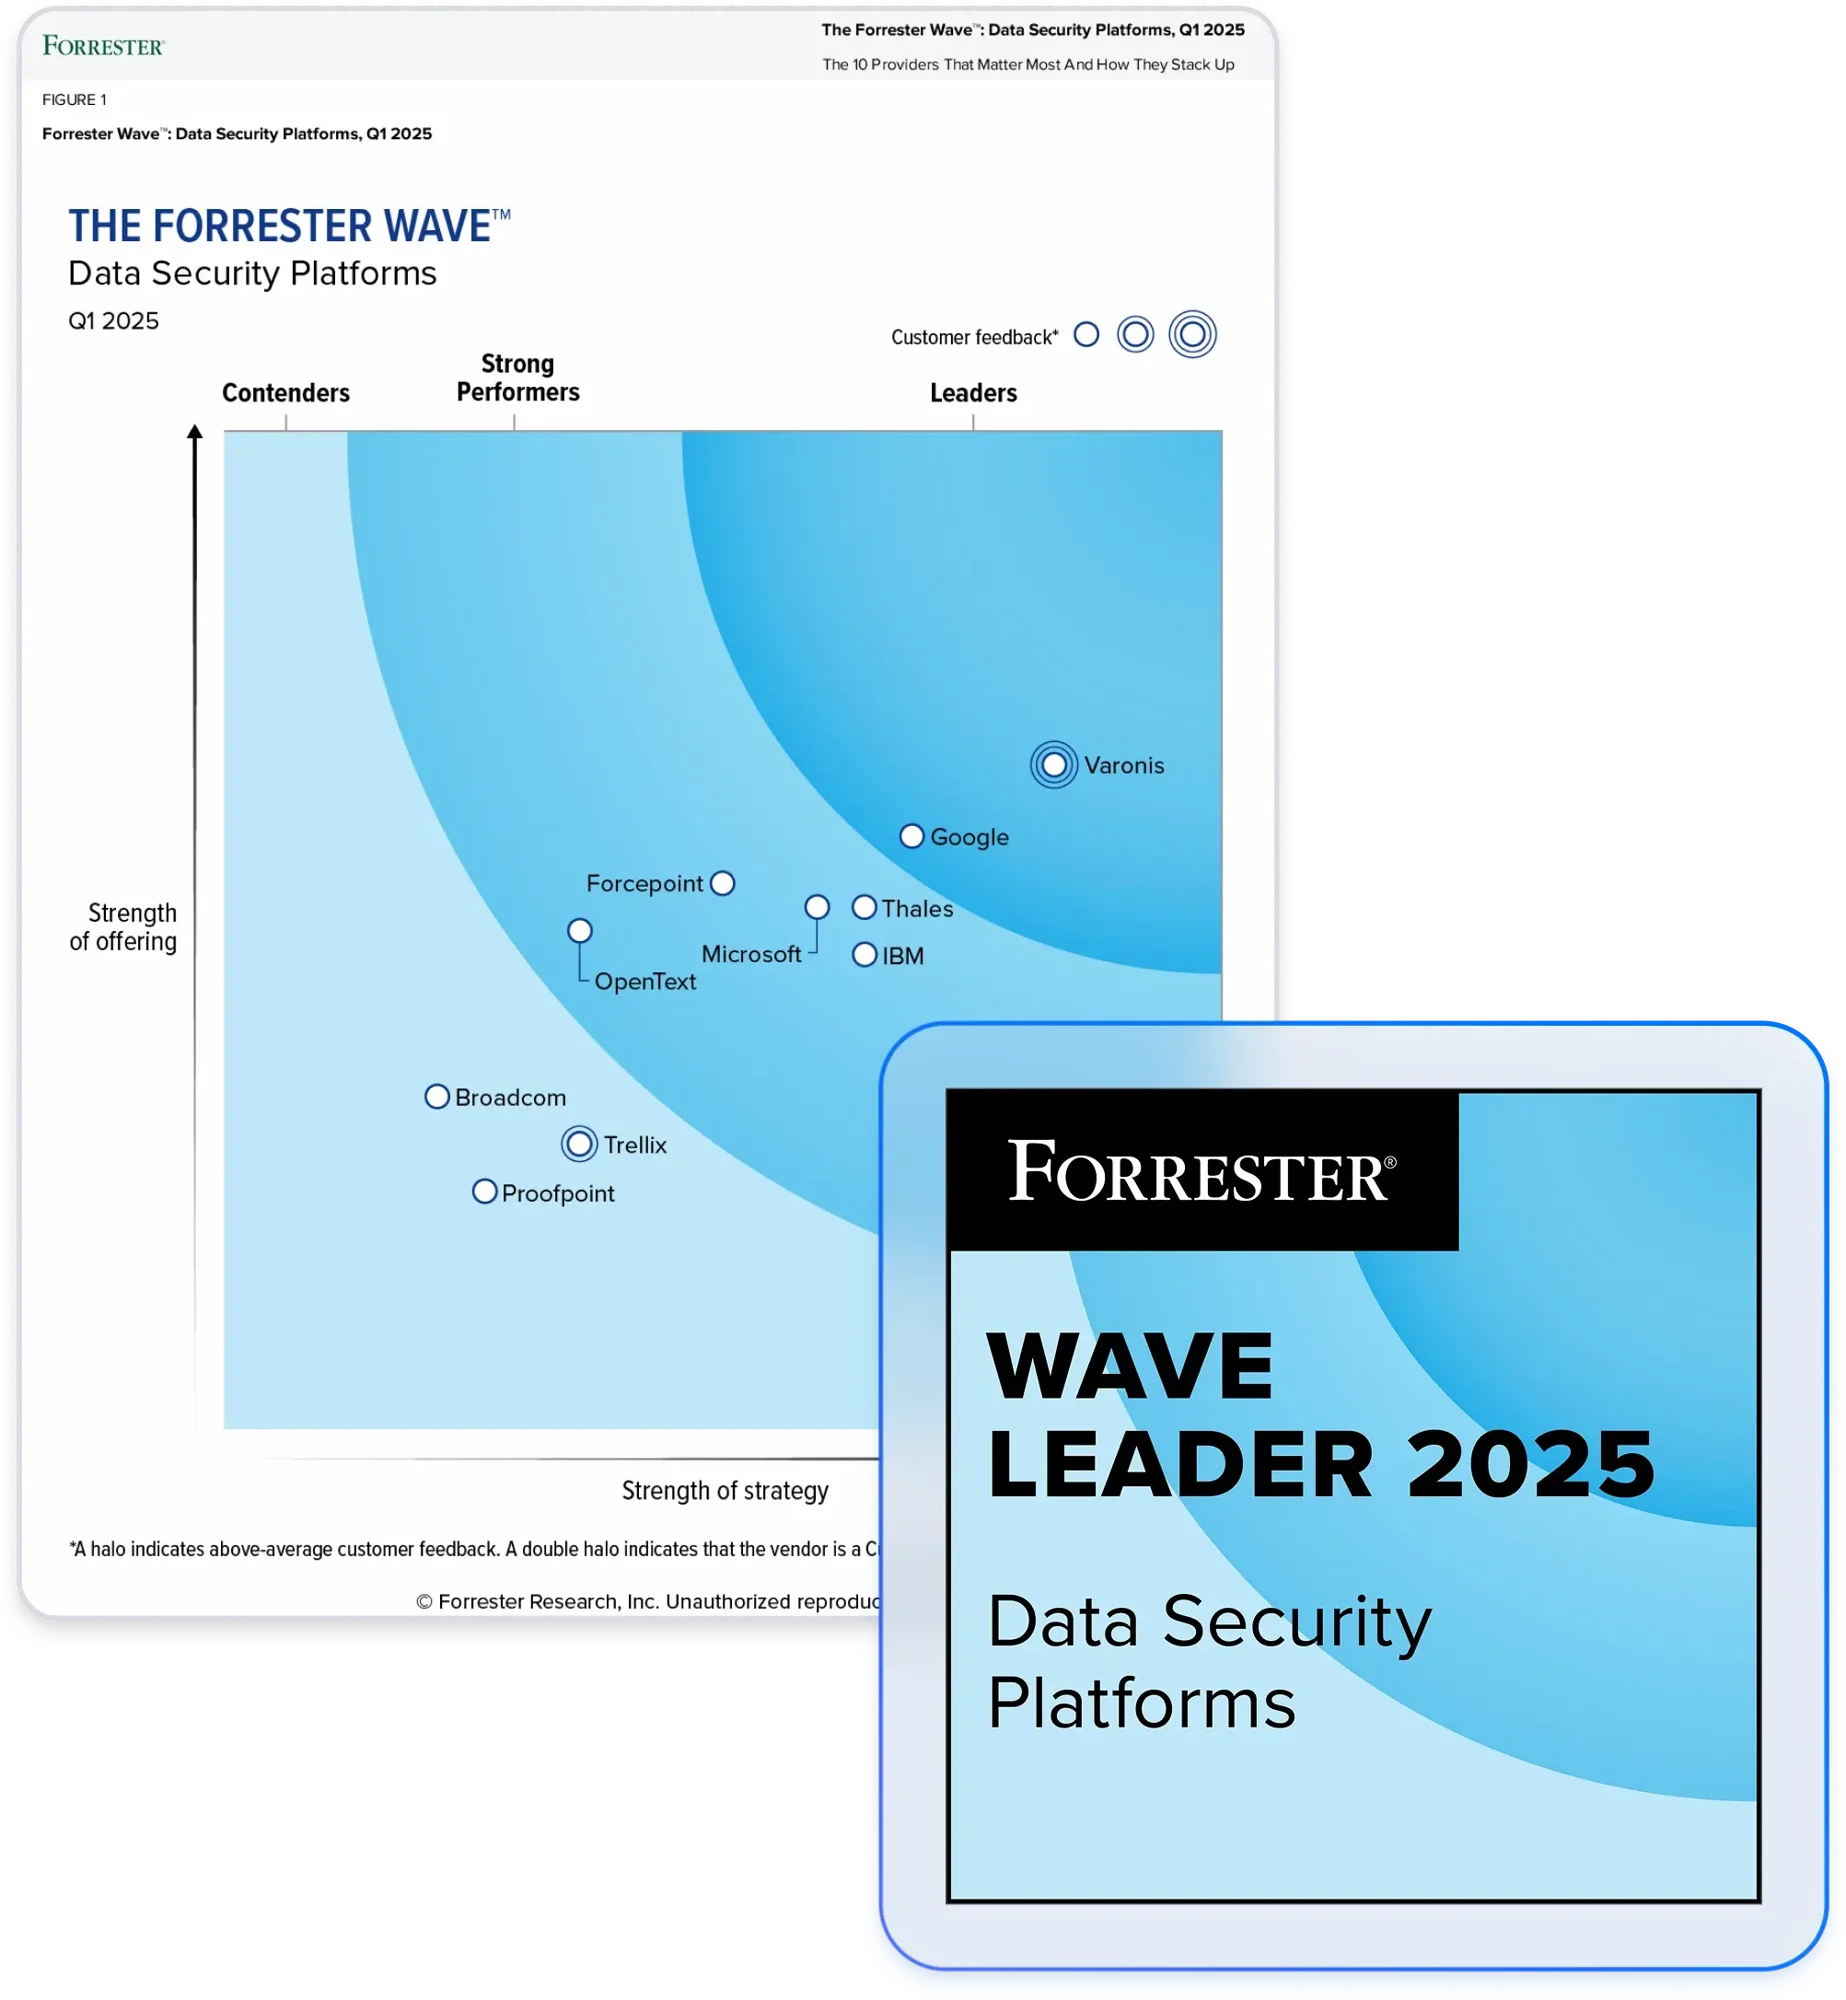
Security teams choose Varonis to find and stop data breaches. See what they say on G2 and why Forrester named us a Leader.

G2
4.6
4.6 out of 5 stars
G2 Leader — Fall 2026G2 Easiest to Do Business With — Fall 2026G2 Momentum Leader — Fall 2026G2 Best Relationship — Fall 2026G2 Users Love Us
See full report
Read the reviews
Forrester Wave Leader 2025, Data Security Platforms
Varonis product overview
auto
image

FEATURED RESOURCES

MDDR Resources

See how our experts find and stop data breaches.

Varonis Triage Agent appears in neon green text against a dark green background

Introducing Varonis Triage Agent: An Autonomous Incident Responder to Amplify MDDR Service

Read blog
Managed Data Detection and Response with Varonis

What is Managed Data Detection and Response (MDDR)?

Data Security
Read blog
shield cover cloud data, Varonis

Varonis MDDR: Industry's First Managed Data Detection and Response Offering

Varonis Products
Read blog
Explore more research

FAQS

Common questions

Book a demo
Sample Incident Report

How is MDDR different from other MDR services?

Most MDRs watch endpoints and networks. They can show how an attacker got in, but not whether data was stolen. MDDR watches the data itself. And breach response is included, not sold by the hour.

What are your response times?

We investigate ransomware in under 30 minutes and all other alerts in under 120 minutes. Both are guaranteed by contract.

Will I get buried in alerts?

No. Our team handles 99% of alerts without involving you. You only hear from us when a threat is real, and a Varonis expert has reviewed every finding.

What happens when there's a breach?

Our forensics team takes over. We scope every compromised user and device, contain the attacker, and report what data was hit. We stay engaged until your objectives are met, however long that takes.

Is breach response really included?

Yes. There are no retainers, hour banks, or report fees. Traditional IR firms often charge $450 to $900 an hour. A single serious investigation can run 250 hours.

Do you only use Varonis data?

No. We use any source you give us access to, including your EDR, SIEM, SOAR, Entra, AWS, and Google Workspace. We also bring our own tools to collect evidence from endpoints and networks.

How fast can we get started?

MDDR is up and running in minutes. Most customers see their first alert in less than a day.

What's in the free MDDR evaluation?

You get the full service, monitoring and breach response, with a security architect who walks you through the findings. If you're attacked during the evaluation, we respond as if you were a customer.

Ready to see MDDR in action?

Book a demo
https://cdn.prod.website-files.com/6aad3cd63e81c645c771a0be/6aad48e61926ad27c8821c7b_varonis-conversion-blue.mp4
https://www.youtube-nocookie.com/embed/717uPD8k5nc