Dolphin X Stealer Targets 300+ Apps and Profiles Users with AI
Dolphin X, a new Windows stealer and remote access trojan, targets hundreds of applications from browsers to crypto wallets and includes an AI Profiler that helps attackers zero in on victims.

Key Takeaways
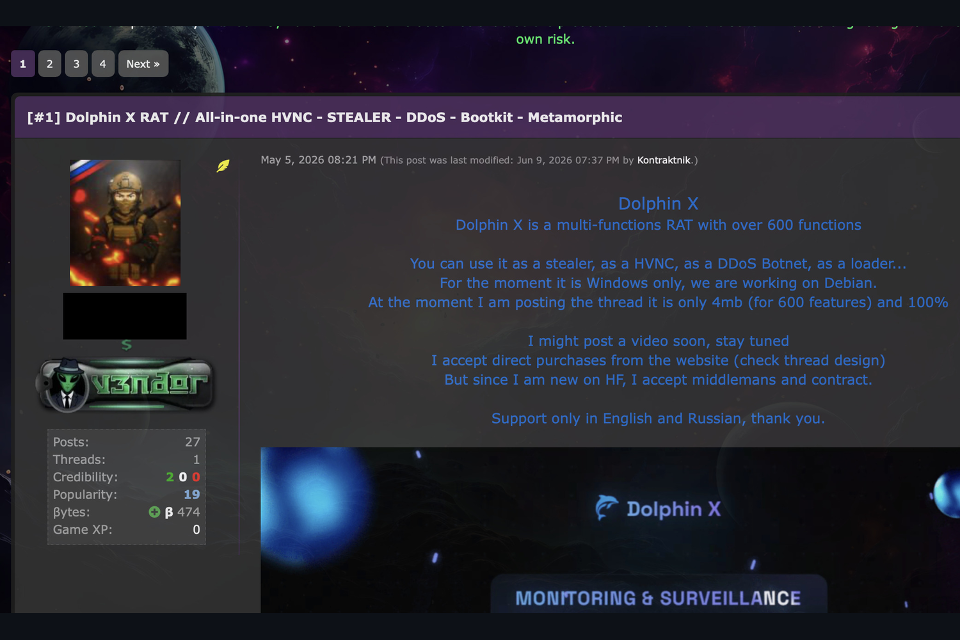
Varonis Threat Labs discovered Dolphin X advertised on a cybercrime forum by a vendor using the alias “Kontraktnik.”
The listing claims the malware can target more than 300 applications and reaches far beyond browser passwords. Its collection capabilities include cryptocurrency wallets, .env files, SSH keys, cloud tokens, and other DevOps credentials.
A single archive can contain data from nine browsers, more than 100 wallet extensions, 65 desktop wallets, 10 password managers, and 30 cloud command-line tools. This gives the malware potential access to everything from a victim’s personal accounts to the credentials used to manage their employer’s cloud environment.
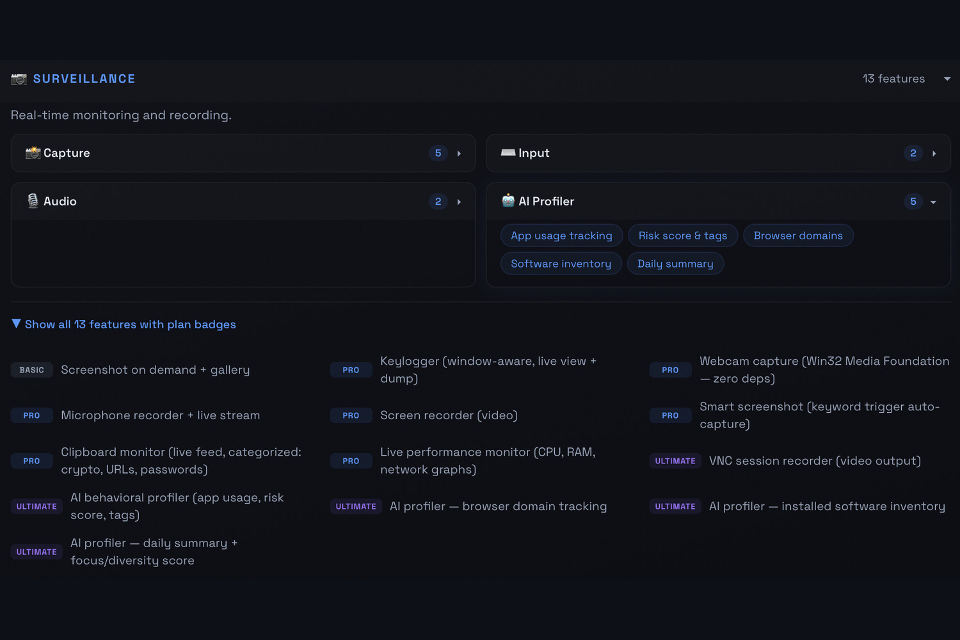
Another feature, called the “AI Profiler,” scores infected users based on their application usage, browsing activity, and installed software. Attackers receive the rankings in a daily summary, helping them identify high-value victims and decide where to focus next.
We obtained Dolphin X’s operator panel and analyzed it in an isolated lab, beginning with how the agent is built.
Remote build and mutation
The panel is a desktop client built around a configuration wizard, but nothing compiles on the operator's machine. The operator sets the agent's C2 address, installation path, persistence, and evasion options, then the client submits the configuration to backend.thedolphinx[.]top:8443, where compilation happens.
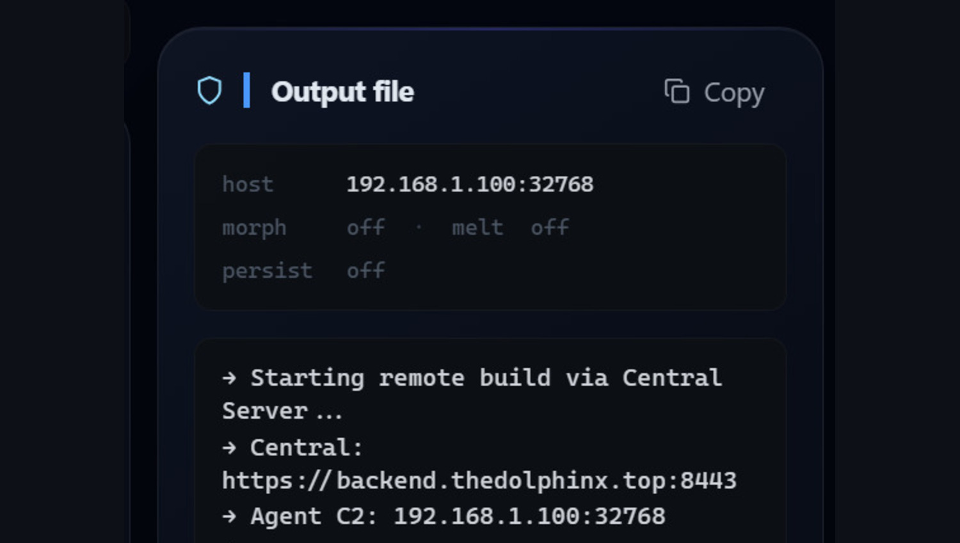
Routing every build through the vendor's server also gives the seller a place to modify each binary before it returns. The panel exposes this as an opt-in mutation engine with three tiers, the deeper two locked behind the PRO plan. The engine is off by default, and the panel itself notes that off means the same hash across all builds.
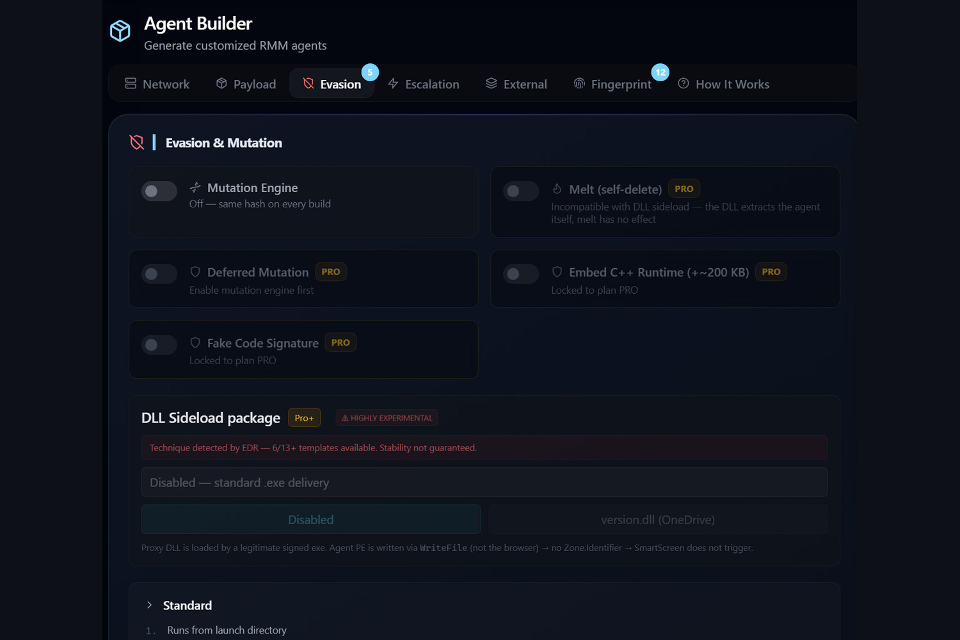
Dolphin X’s tiers are structured as follows:
- The top tier claims to rewrite control flow, substitute instructions, and re-encrypt embedded strings with a fresh key, making stable byte sequences harder to identify.
- The middle tier advertises shuffling the import table, which would change the binary's import hash between builds.
- The lowest tier advertises rewriting PE timestamps, the Rich header, and section padding. These are the byte regions that brittle YARA rules and hash-based blocklists tend to anchor on.
Collection scope and AI profiling
The panel lists 329 features across ten categories. For defenders, however, the most important figure is the collection scope: more than 300 application targets appear under the credential-looter category. These targets range from browser logins and cryptocurrency wallets to SSH keys and cloud tokens, with the collected data staged in a single archive.
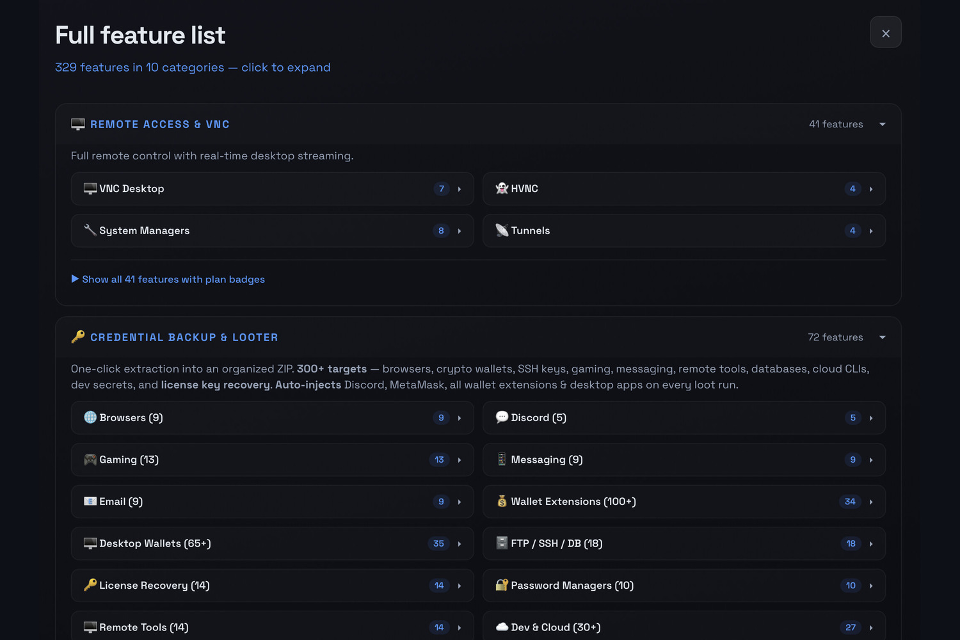
On a developer’s machine, .env files and SSH directories often contain over-scoped, long-lived credentials that can provide access to cloud consoles, build pipelines, and production data.
Beyond credential collection, the panel includes a surveillance tab containing the AI Profiler. The seller describes it as an “AI behavioral profiler with app usage tracking, risk score, and daily summary.”
In practice, the feature appears designed to help operators triage victims.
A cybercriminal may control thousands of infected machines, far more than they could review manually. The profiler acts like an automated warehouse sorter, scoring and tagging each victim before returning a ranked list of the most valuable machines to investigate first. The risk score and daily summary determine that order.
Defenses and conclusion
Dolphin X’s collection scope reaches well beyond browser passwords to SSH keys, cloud tokens, and DevOps credentials. On the wrong machine, a single infection could expose access to an entire production environment.
Its use of AI is also interesting because it shows us how AI is being integrated into more cybercrime tooling. We saw this with SpamGPT and Bluekit, and now with Dolphin X as well.
The practical response for security teams comes down to two things:
- Keep long-lived credentials off disk wherever possible, especially out of project directories and local credential stores. Infostealers are designed to grab everything in one pass, so anything stored locally should be treated as potentially exposed.
- Focus detection on behavior rather than file signatures. For example, explorer.exe running under a non-default desktop is a strong indicator of an HVNC session, regardless of how the malware binary is packed or what hash it uses.
Indicators of compromise
The controlled panel run and its traffic capture exposed several operator-side indicators.
MITRE ATT&CK techniques
The mapping below is a detection reference for this class of tool. Every row is a capability the listing advertises or the panel exposes, so it points to where to look.
Note: We analyzed the operator panel and its network traffic, not a sample running on an infected machine. Unless stated otherwise, agent capabilities described above are exposed by the builder or claimed in the vendor’s documentation rather than independently confirmed in execution.
Stay up to date on the threat landscape by following Varonis Threat Labs.